Staff & Access Control
The right people, with the right access, at the right time.
Each user has their own secure account, with rights defined per excavation and per user. Every change is tracked and automatically attributed to its author, for transparency, accountability, and contribution tracking from field to publication.
Permissions that match
how excavations really work
Five levels of authorization
Program administration, excavation administration, form management, data entry on site, data consultation. Rights are assigned individually and granularly by your own designated administrators: the principle of least privilege, built in.
Per excavation, per user
The same person can be an administrator on one intervention and a data-entry user on another. Access follows the role on each project, not a global label.
Users only see what's theirs
Each user sees only what is relevant to them and can only act within their permissions, greatly reducing the risk of errors or accidental data deletion.
Grant access, without losing control

Guests without risk
Grant temporary read-only access to third parties (researchers, students, partner institutions) without compromising the confidentiality of anything else.

Dedicated workspaces
Each institution works in a fully isolated environment. Shared spaces can be opened for cross-institutional collaborations. You decide what is shared, and with whom.

Teams as they really are
Permanent staff, external specialists, temporary excavation workers: add them, scope their rights, remove them when the campaign ends.
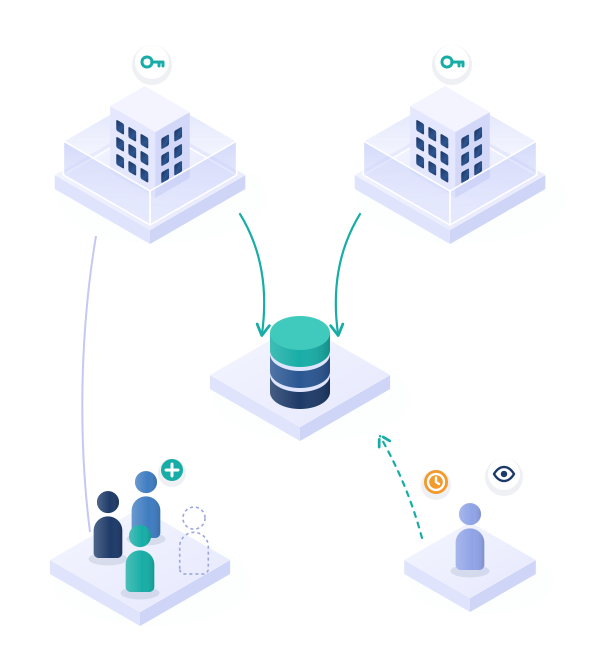 Your workspace
Partner workspace
Shared space
Campaign team
Read-only guest
Built for fieldwork
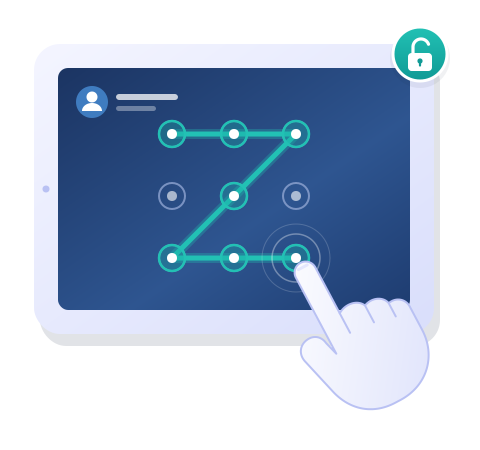
One tablet, many hands. A graphical password system lets archaeologists switch accounts in seconds when several people share a device on site, so every entry is still attributed to the right person, without typing passwords.
Accountability, end to end
Everything attributed
Every creation, modification, and deletion is timestamped and attributed to its author.
Full edit history
Earlier versions of any record remain accessible in read-only mode; previous values of any field can be consulted.
Available for the life of
your contract
The application audit trail stays open to your administrators throughout.
Editorial roles too
The Publication module carries the same logic into publishing: authors, organization administrators, and publication administrators each act within a defined workflow.
Security foundations
Access control rests on a hardened base: Swiss-hosted infrastructure, encryption in transit and at rest, and single sign-on (SSO) available to all clients.
How we store and protect your data
Fewer errors, by design
People can only touch what they're meant to touch, so accidental deletions and mix-ups drop accordingly.
Collaboration without exposure
Third parties, partners, and students get exactly the view they need, and nothing more.
Accountability that builds trust
Every contribution attributed, every change reversible, every action traceable.
Ready to give everyone exactly the access they need?
Free calibration to your methodology.
Free field test. No commitment.